Mock APIs with real authentication
The backend isn't ready.
Your frontend doesn't have to wait.
MockLab gives frontend and mobile developers live mock APIs that behave like the real thing — signed JWT logins, protected endpoints, conditional responses and network delay. Live at a public URL in under a minute.
Free while in beta. No credit card required.
# 1. Log in — MockLab issues a real signed JWT
$ curl -X POST https://api.mocklab.studio/mock/acme-shop/auth/login
{ "accessToken": "eyJhbGciOiJIUzI1NiIs…", "expiresIn": "15m" }

# 2. Use it on a protected endpoint
$ curl https://api.mocklab.studio/mock/acme-shop/orders \
    -H "Authorization: Bearer eyJhbGciOi…"
200 { "orders": [ … ] }

# 3. No token? Rejected, like a real API
$ curl https://api.mocklab.studio/mock/acme-shop/orders
401 { "error": "Unauthorized", "message": "Missing Bearer token for Dynamic JWT" }
See it in action
Screenshots from the app, not mockups.
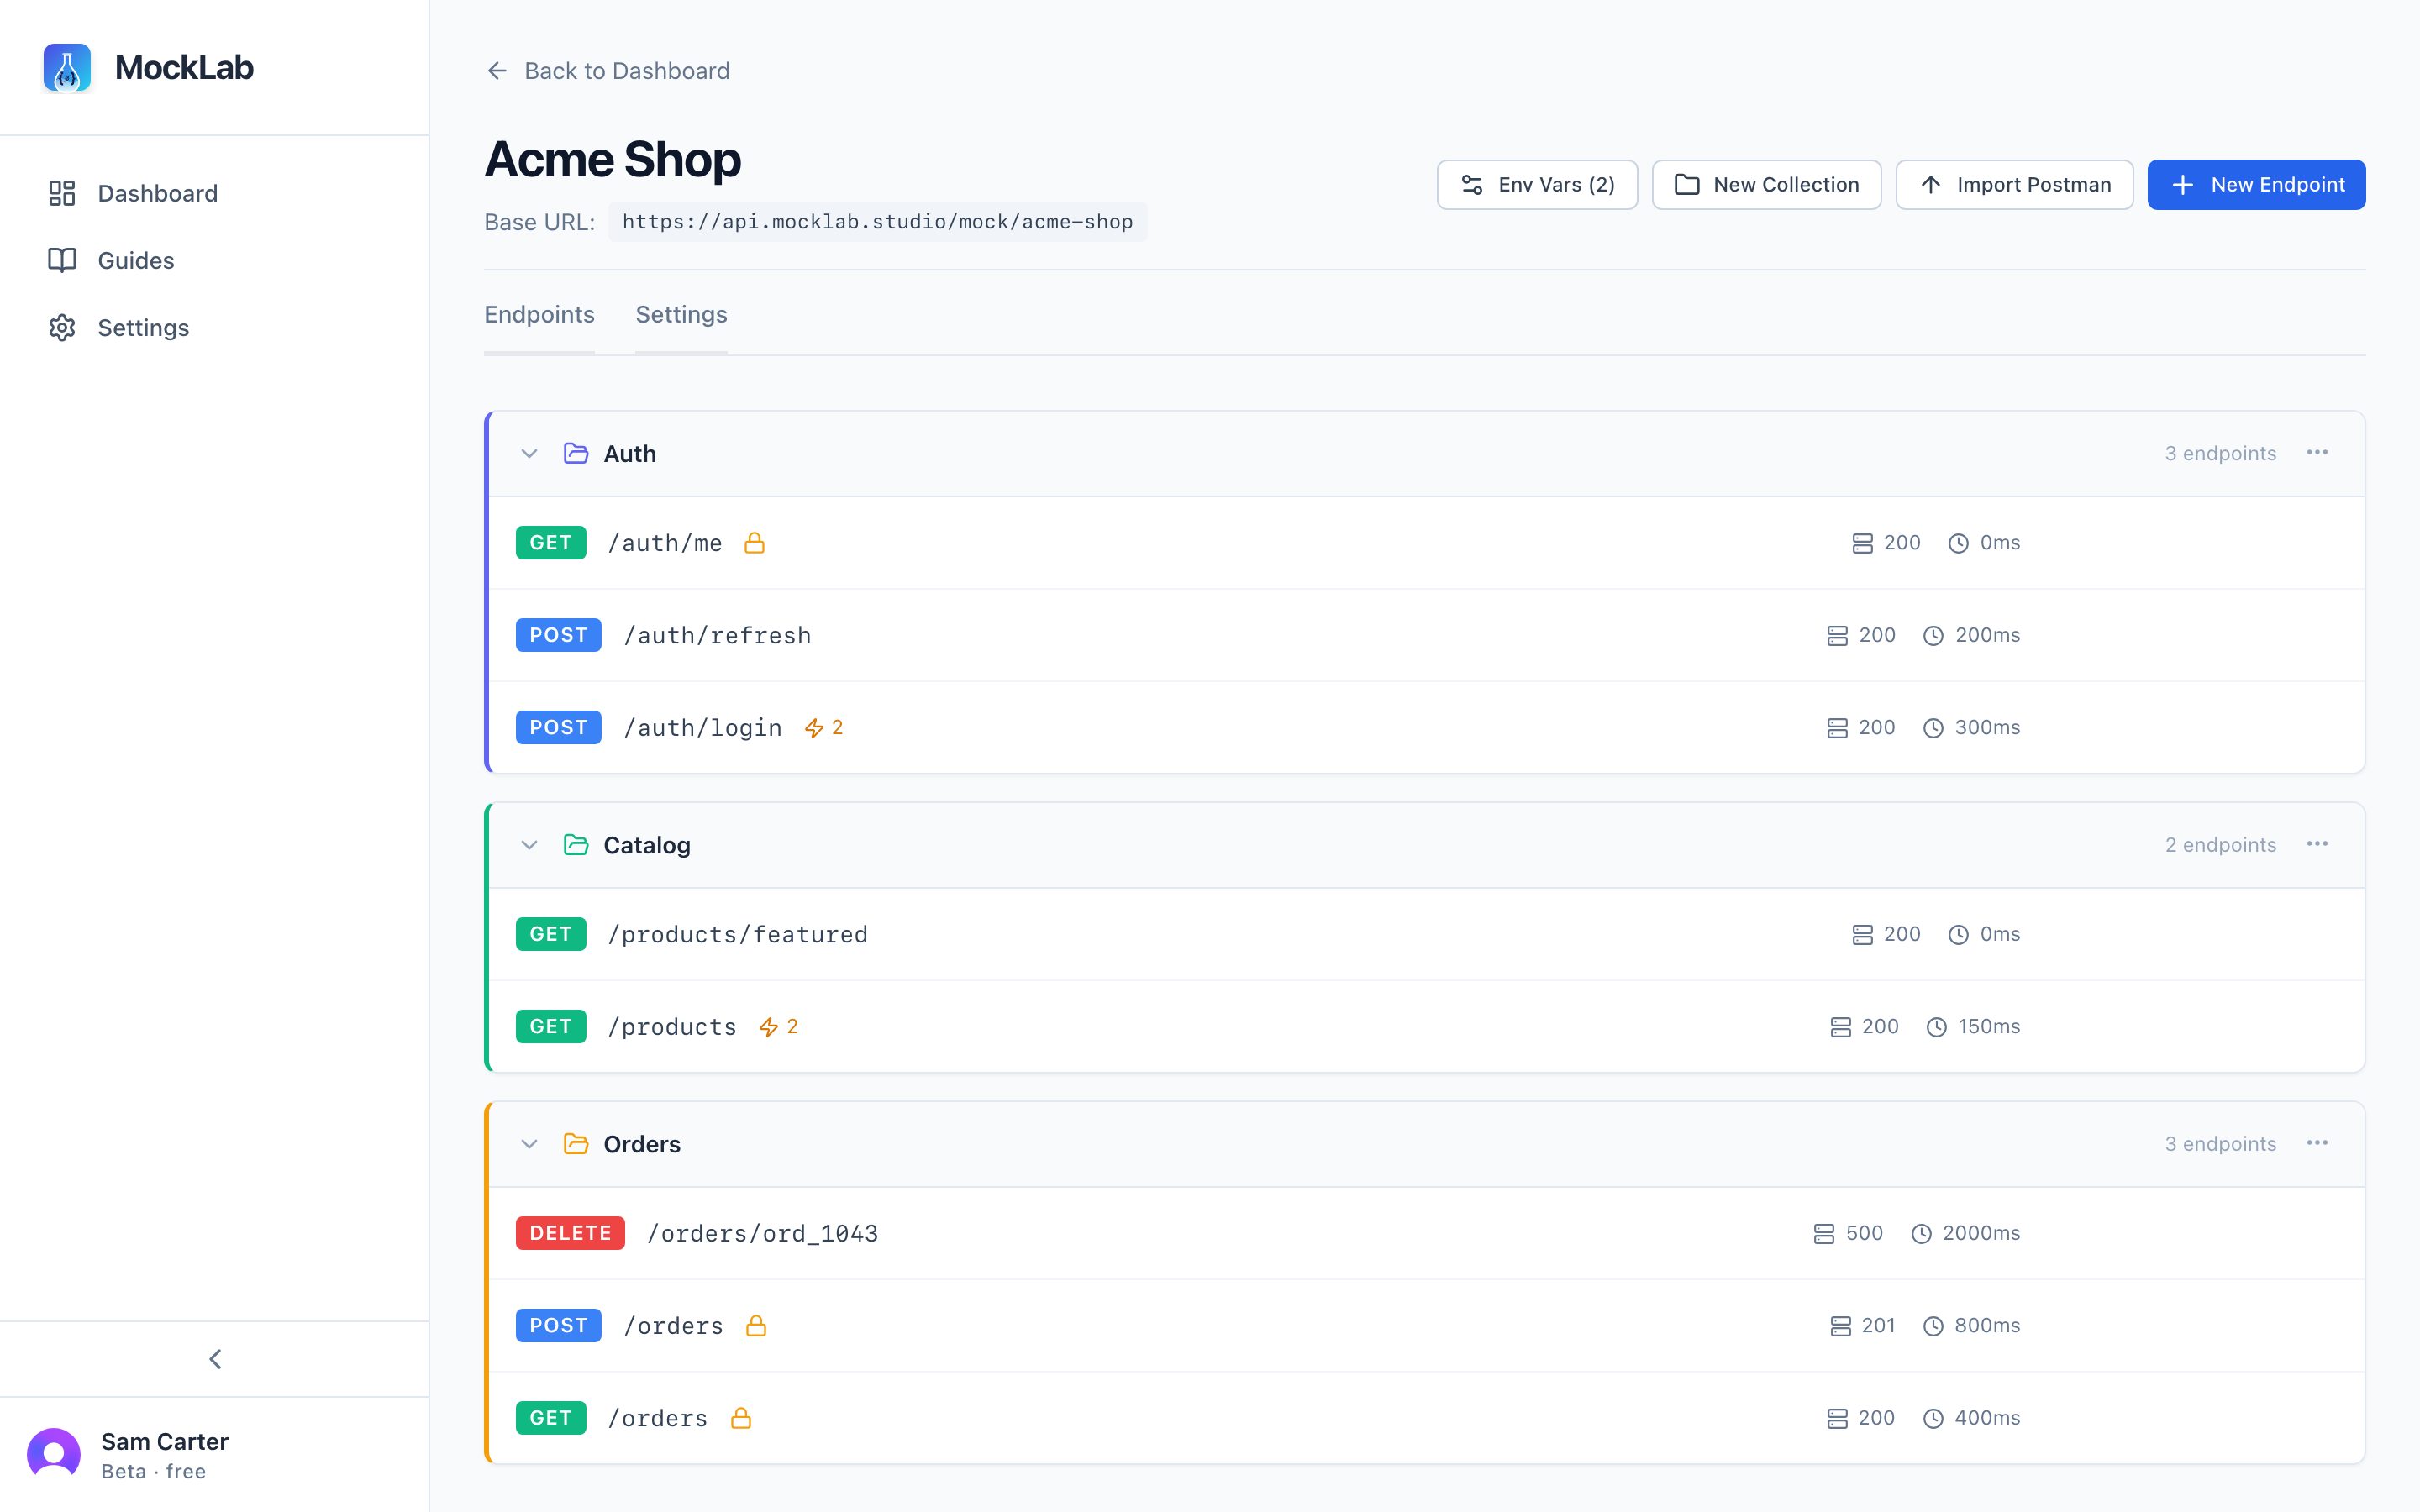
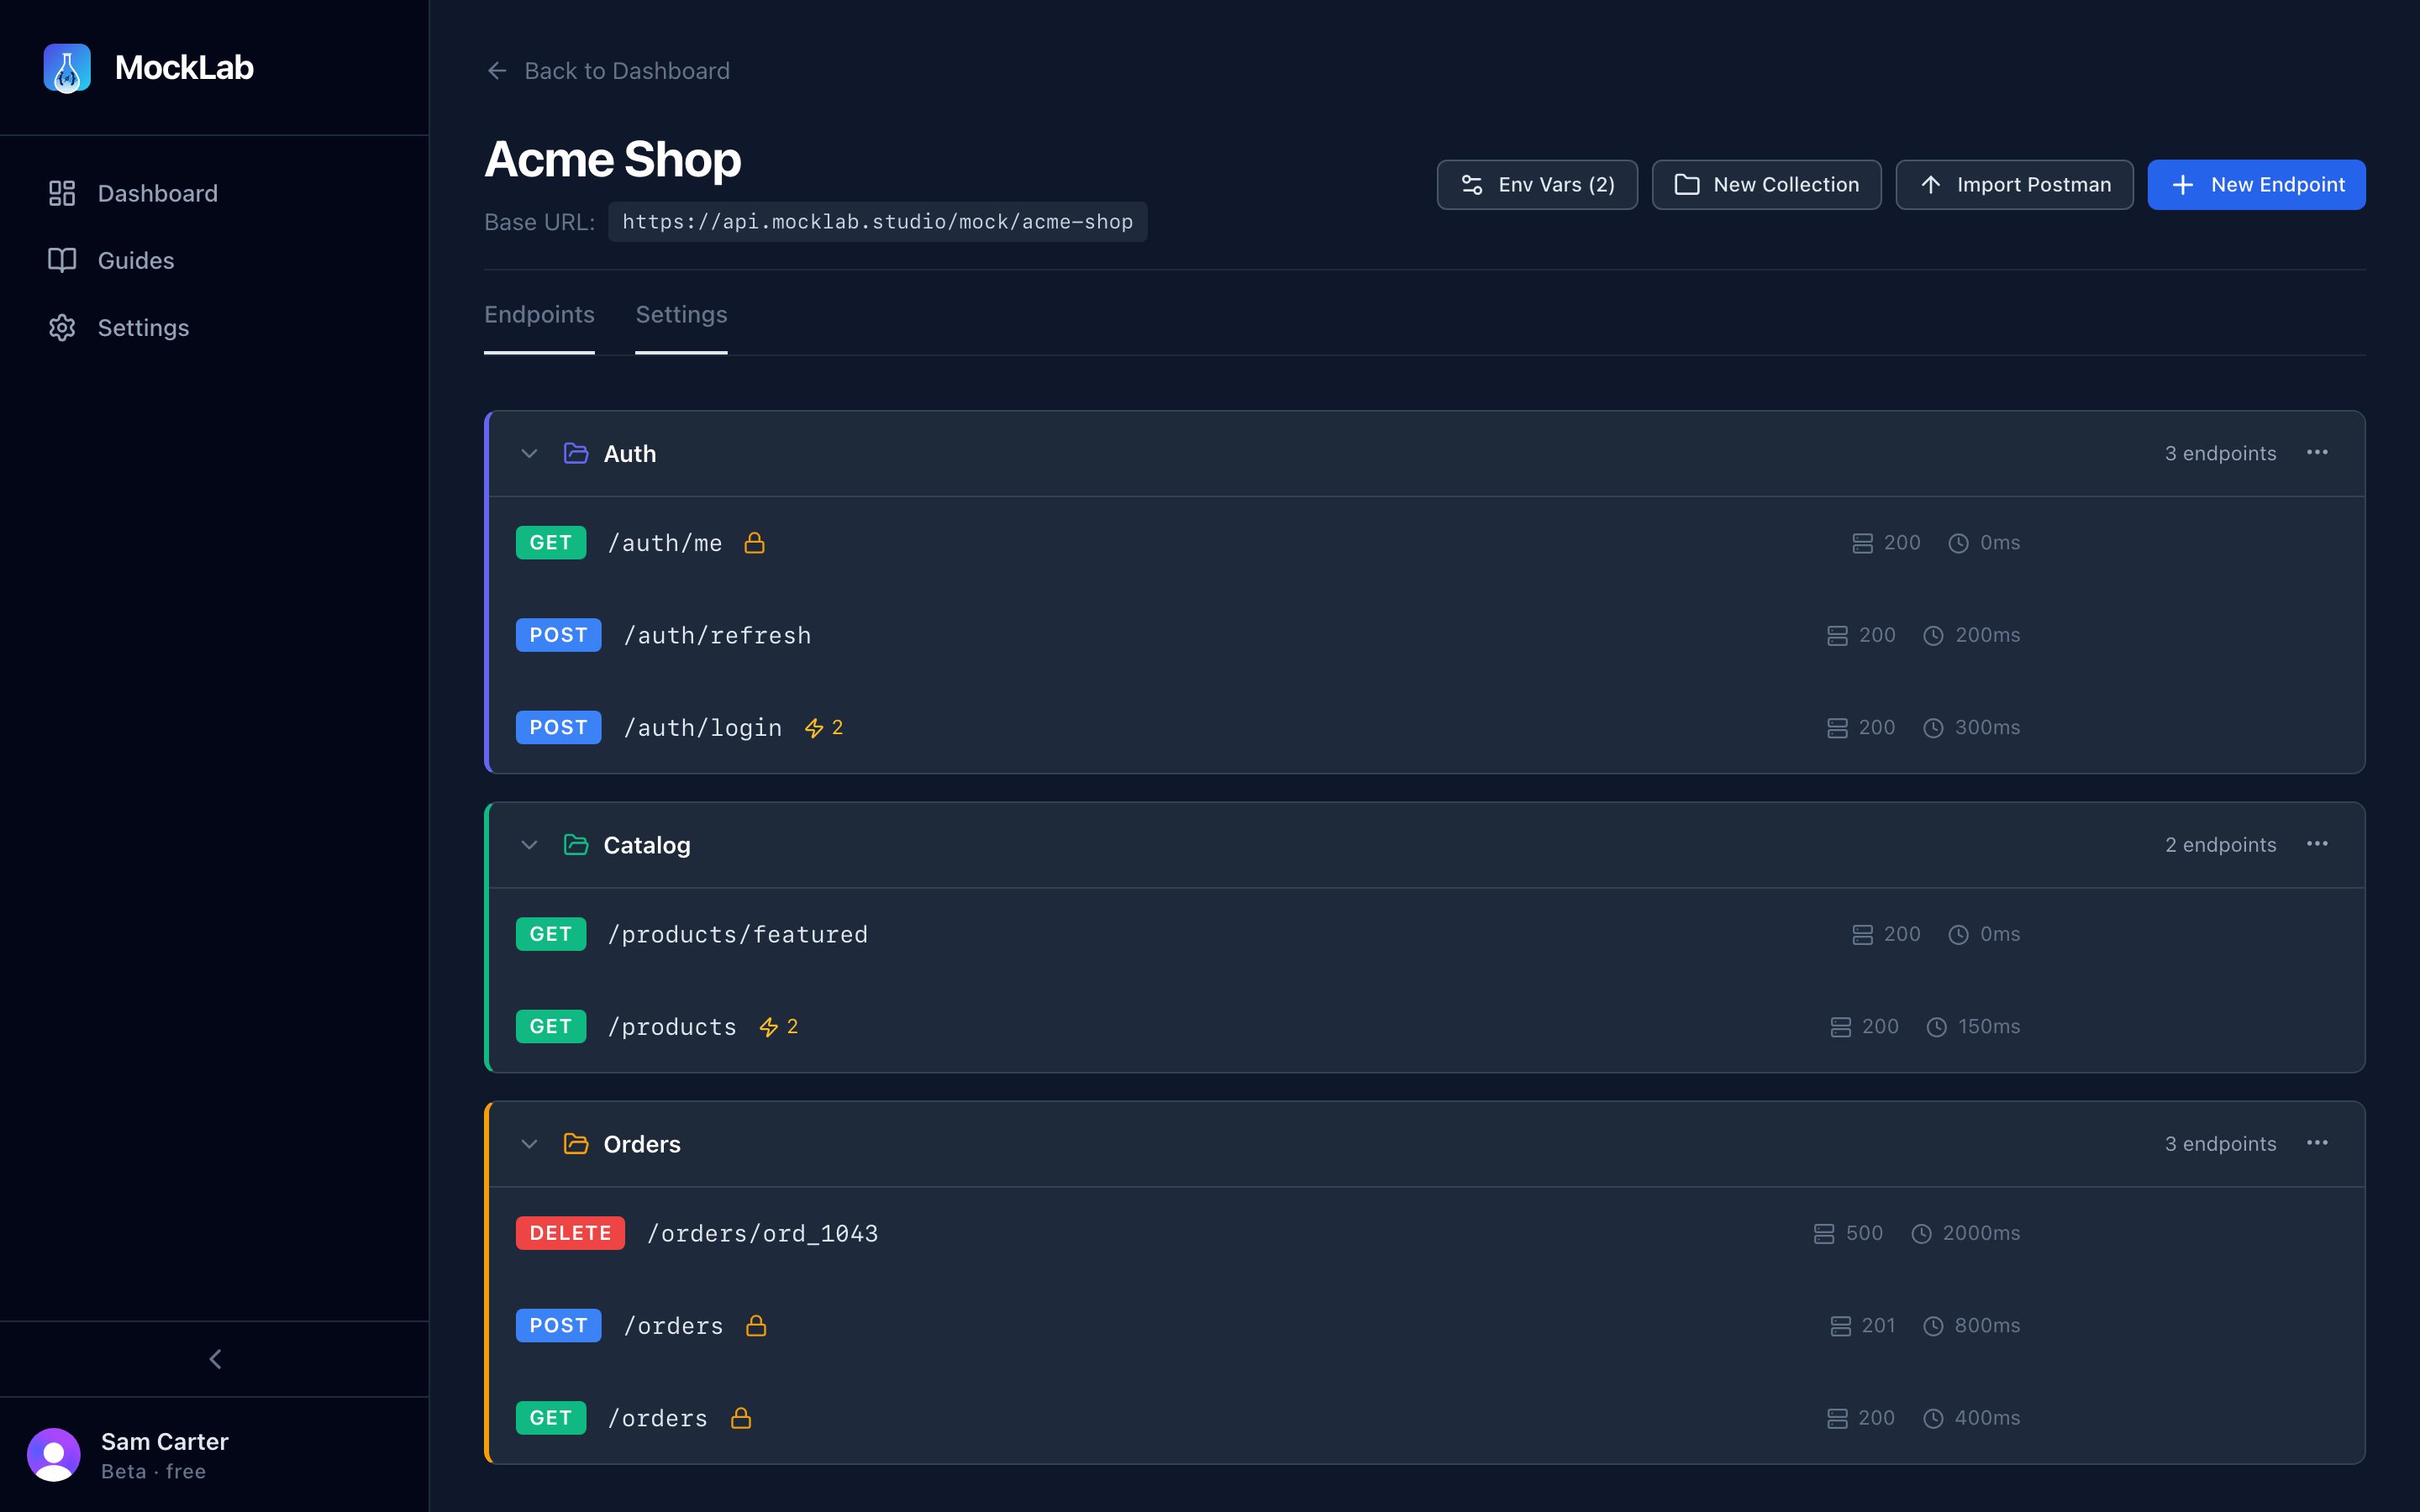
Every endpoint live at a public URL
Group endpoints into collections, see status, delay, auth and variants at a glance, and call them from any app, phone or CI job.
From idea to live endpoint in three steps
No server to run, nothing to install.
- 1
Create a project
Name it and MockLab gives it a slug. Every endpoint in the project lives under that slug.
- 2
Define endpoints
Pick a method and path, write the JSON in the editor, and set the status code. Add auth, variants or a delay when you need them, or import a Postman collection.
- 3
Call the live URL
Point your app at the mock URL and build. When the real backend ships, swap the base URL.
More than static JSON
Most bugs live in the flows around the data — logging in, expired sessions, errors and slow networks. MockLab lets you build those before the backend exists.
Real JWT login flows
Return {{$jwt.access:15m}} from a login endpoint and MockLab issues a signed, expiring token. Protected endpoints accept only valid tokens from your project, so token storage, expiry and refresh logic get tested for real.
Auth that actually rejects
Require a Bearer token, an API key header or Basic auth on any endpoint. Missing or wrong credentials get a 401 (or any status and body you choose).
Response variants
One route, many outcomes. Match on a query param, body field or URL segment to return a different status and body — success, empty and error states without extra endpoints.
Simulated latency
Add a delay of up to 10 seconds to any endpoint to see your loading states, skeletons and timeouts the way users will.
Project variables
Define values like {{currency}} once and reference them in every response. Change one value, every endpoint follows.
Postman import
Already have a Postman collection (v2.0 or v2.1)? Import it and get the matching endpoints and folders in seconds.
A mock that behaves like an API
A static JSON mock answers every request the same way. MockLab responds to who is calling and what they sent.
| Capability | Static JSON mock | MockLab |
|---|---|---|
| Live public URL for each endpoint | ||
| Custom status codes and JSON bodies | ||
| Issues real signed, expiring JWTs | ||
| Rejects missing or invalid credentials | ||
| Different responses based on the request | Extra endpoints | |
| Configurable response delay | Sometimes | |
| Shared variables across responses |
Frequently asked questions
What is MockLab?
MockLab is a hosted mock API server for frontend and mobile developers. You define endpoints with a method, path, status code and JSON body, and each one is instantly live at a public URL you can call from your app.
Can I mock an API that requires authentication?
Yes. Any endpoint can require a Bearer token, an API key header or Basic auth, and returns a 401 (or the status you choose) when credentials are missing or wrong. You can also issue real signed JWTs from a login endpoint and require them on protected endpoints.
How do mock JWTs work?
Put {{$jwt.access:15m}} or {{$jwt.refresh:30d}} in a response body and MockLab replaces it with a signed JWT that expires after the duration you set. Endpoints protected with the MockLab JWT auth type accept only valid, unexpired tokens issued by the same project.
Can one endpoint return different responses?
Yes. Response variants return a different status code and body when a query parameter, request body field or URL segment matches a value, so you can test success, empty and error states on the same route.
Can I import my existing Postman collection?
Yes. Import a Postman collection (v2.0 or v2.1) and MockLab creates the matching endpoints and folders in your project.
Is MockLab free?
Yes. MockLab is free to use right now and no credit card is required to sign up.
Stop waiting on the backend
Build your login, error and loading states today against an API that behaves like the real one.